
PHP2Shell support from Secarma
Understand your exposure. Take action with confidence.
Tell us your current cyber challenges


PHP2Shell is a family of critical vulnerabilities in PHP, the technology behind many websites and business applications. Because the weaknesses sit within PHP itself, even applications with secure code can be affected.
Under affected conditions, an attacker could run code on a server or access sensitive information without needing an account. Researchers demonstrated attacks against WordPress, Drupal and Joomla, but other PHP applications can also be affected.
Successful exploitation could expose passwords, authentication tokens and other sensitive data. It could also disrupt websites and applications, affecting your operations and customer confidence.
Knowing which installations are vulnerable helps you prioritise action. Secarma gives you the visibility and support to move from uncertainty to remediation.
Start with Secarma Asset Management, free to install
We will deploy our Secarma Agent on supported devices, giving you insight into your assets and their security posture. This provides the foundation for understanding and managing your exposure.
Identify exposure with the PHP2Shell add on
Our optional PHP2Shell add on will identify PHP installations across your enrolled estate and assess whether they are vulnerable, showing your team where action is needed.
Deploy patches with confidence
We can support you in deploying available security patches to supported installations, with the scope and approach agreed around your operational needs.
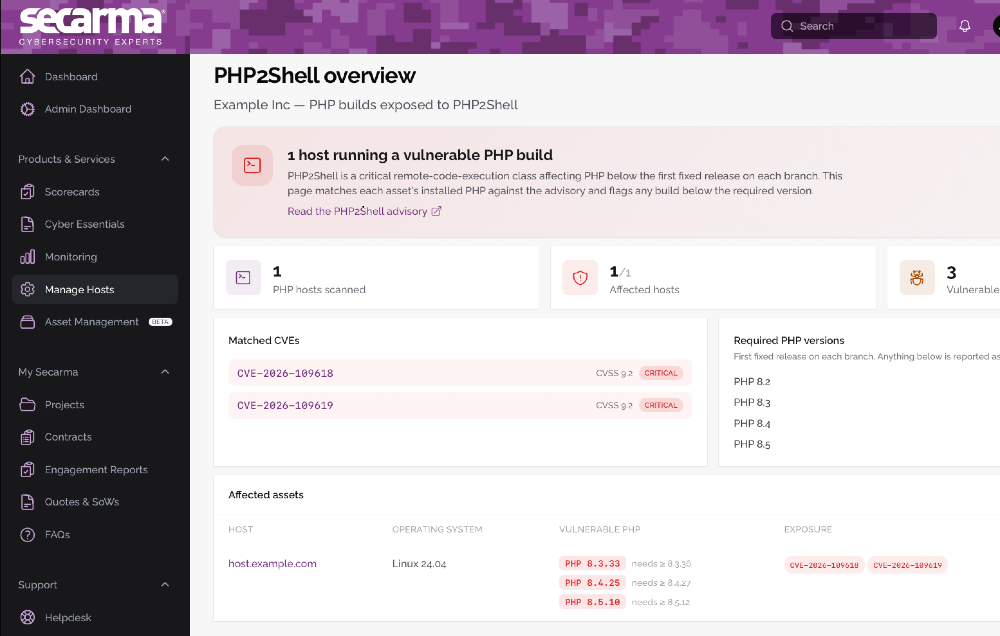
Our team will help you understand the findings and prioritise the next steps. We will work with you to coordinate service restarts, check that applications operate as expected and guide relevant configuration changes.
You gain clear advice and practical support from a trusted cybersecurity partner.
Take the first step towards clearer visibility
Get Secarma Asset Management for free and speak to our team about adding PHP2Shell assessment and patch deployment.
Speak to an Expert Today
Call us on 0161 513 0960 or email actnow@secarma.com
Measure Maturity. Identify Gaps. Build Resilience.


Secure Your Supply Chain. Protect What Matters.

Scalable security support, built around your business.

Strengthen Your Response Before a Real Attack Hits.

Plan Securely. Develop with Confidence.

Align your privacy practices with ICO standards.

Simulate, Measure, and Strengthen User Awareness.

Understand where you are. Identify the gaps. Build a clear path towards certification.

Measure resilience. Identify gaps. Build confidence.
Test your ISMS. Identify issues early. Approach certification with confidence.
Understand your exposure. Take action with confidence.










Secarma Limited (Company no. 04217114, registered in England & Wales)
Registered office: 3 Archway, Birley Fields, Manchester, M15 5QJ
VAT no. GB 775 7144 00